
Searches for buy Gmail accounts with app password usually come from people trying to connect email to a compatible application or workflow. An app password is not a universal login and is not available for every Google account or every security configuration. Before choosing any account service, understand the feature, confirm that your intended application supports it, and consider whether a managed account is a better fit.
What Is a Gmail App Password?
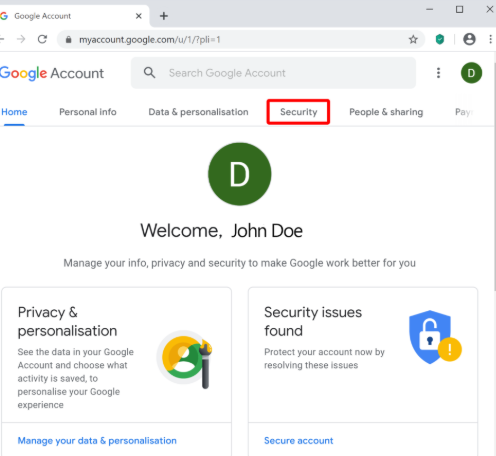
An app password is a separate, generated password that can let certain applications access a Google account when the application cannot use the normal modern sign-in flow. It is different from the account’s regular password and is not intended to replace two-step verification. Availability depends on Google’s current account security requirements and configuration; some accounts, organizations, or protection settings may not offer app passwords. That means a listing that advertises an app password should not be treated as a guarantee that the feature will work indefinitely. Confirm the current requirements in Google’s official help information before planning a workflow around it. Never treat an app password as a way to skip security checks or gain access to an account you do not control. Use it only with applications and accounts for which you have authorization.
Check Application Compatibility First
Before obtaining any account, identify the exact email client, device, or software you need to connect. Some applications support Google’s official sign-in screen and permissions flow; others rely on older authentication methods. Prefer modern sign-in with OAuth when the application supports it, because it avoids sharing the account password directly with the application. Check the software’s documentation for supported authentication methods, required server settings, and any organization-level restrictions. If a client says it needs an app password, verify that this is still its recommended approach rather than an outdated workaround. A technically incompatible account will not become compatible simply because a seller includes a password. Testing the workflow with an account you legitimately control can reveal problems before you move important communications. If you compare listings for Gmail PVA accounts, review the stated terms and recovery arrangements before deciding.
Understand the Security Trade-Offs
App passwords can be convenient for compatible applications, but they also create a credential that must be protected. Anyone who obtains a valid app password may be able to access some account functions until that credential is revoked or blocked. Store credentials in a secure password manager or an appropriate secrets manager, not in a public document, source-code repository, or shared spreadsheet. Do not send passwords through public chats, and do not paste them into untrusted websites. If an app or device is retired, remove its access and revoke the associated app password where the account settings allow it. Use unique credentials, review security activity, and keep recovery details current. For a business, establish a process for revoking access when a device is lost or an employee leaves.
Be Careful with Third-Party Account Offers
A seller’s claim that an account includes an app password does not establish who controls the recovery methods or whether the account will remain available. The account may still be subject to additional verification, security review, or restriction. Ask what is actually included, whether access is exclusive, and whether the seller retains recovery information. Never provide the seller with your existing Google password or security codes. Do not assume that a delivered credential proves ownership or that it can be used for every application. Also review Google’s terms and the policies of the service where you intend to use the account; transferring consumer accounts may create policy or continuity risks. For a long-term business workflow, managed accounts under your organization’s control are generally easier to secure and recover.
Troubleshoot App Password Problems Safely
If a connection fails, first confirm the username, the selected authentication method, and the client’s current documentation. Check whether Google requires a modern sign-in flow, whether an administrator has disabled the feature, and whether the account has a security alert or pending verification request. Avoid repeatedly trying random credentials or disabling protections to force a connection. Update the application, remove obsolete saved credentials, and generate or revoke app passwords only through official account settings when the feature is available to the legitimate account owner. Review the client’s error message carefully: an authentication error may be different from a server, network, or configuration error. For work accounts, contact the organization’s administrator rather than changing controls without authorization.
Choose the Most Sustainable Setup
If the goal is to connect email to business software, compare the official options before relying on transferred accounts or static credentials. Gmail’s supported sign-in flow, Google Workspace administration, role-based addresses, aliases, and approved integrations may offer better security and clearer ownership. Keep a list of applications that can access each inbox, document the purpose of each connection, and review permissions periodically. Make sure important email is retained according to your business requirements and that recovery does not depend on a person outside your organization. An app password is only one technical mechanism; it is not a guarantee of account quality, ownership, or uninterrupted service. Select a solution based on compatibility, security, recoverability, and compliance with the rules of the services involved.
Where possible, prefer an application’s official Google sign-in option instead of entering a static password into a third-party client. Modern authorization can allow access to be reviewed and revoked without sharing the main account password with the application. If a software vendor insists on an older method, check its current documentation and security guidance before proceeding. Do not install unknown utilities or browser extensions that claim to generate credentials or make an account compatible; they can expose the inbox or device to additional risk.
For a work environment, write down which application needs access, what information it will read or send, who approved the connection, and how access will be removed. Limit permissions to the minimum needed for the task. Review the connection after software updates, employee changes, or a security alert. If an app password is exposed, revoke it through the official account settings when possible and review recent account activity. Treat the credential as sensitive even if it is different from the account’s primary password.
Do not confuse successful sign-in with long-term reliability. A connection may work during setup but fail later because the account’s security configuration changes, an administrator updates a policy, or the application changes its supported authentication methods. Test the workflow with non-critical messages first, document any configuration, and keep an alternative contact route available. For business-critical communications, choose a supported setup with clear administrative control rather than relying on one static credential or an account whose recovery details are outside your organization.
Before putting a connection into production, test the complete workflow with ordinary, non-sensitive messages and confirm that the application behaves as documented. Keep a record of the approved setup, the person responsible for it, and the steps to revoke access. Revisit the setup whenever Google or the software vendor changes its authentication guidance.
Also make sure that the person responsible for the workflow knows how to recognize an authentication error, a security warning, and an ordinary network problem. Different causes require different fixes, and repeatedly changing passwords without understanding the error can make troubleshooting harder.